
AI-Powered Cybersecurity · EMSPakistan-IT (Pvt.) Ltd.
AI-Powered Penetration Testing & VAPT Services
Powered by our in-house AI testing engine, AI Bug Hunter
The bug that breaks your business won't trigger an alert.
16+ years in AI & security · SECP & PSEB registered · UNGM listed supplier · CAISR certified · Serving Pakistan, UAE & worldwide
For Preferred Section of Service: Click a Button Below.
🔥 Not Just Claims — Proven Research. Published Results. Industry Leadership.
Know What You're Buying
What is VAPT?
VAPT stands for Vulnerability Assessment & Penetration Testing — two layers of security testing. Most vendors sell one and call it the other. Here’s the honest difference.
Vulnerability Assessment (VA)
Automated + light manual scanning to find and list known weaknesses across your systems. Broad coverage, fast turnaround.
- Wide scan of your attack surface
- Known CVEs, misconfigurations, exposed services
- Prioritized findings list
- Best for a quick, budget-friendly health check
Penetration Testing (Full VAPT)
Certified experts actively exploit weaknesses — including business-logic flaws automated tools never catch — to prove real-world impact.
- Manual exploitation & chaining of vulnerabilities
- Business-logic bugs: IDOR/BOLA, auth bypass, workflow abuse
- Proof-of-concept for each critical finding
- Best when you need real assurance or compliance sign-off
Why EMSPakistan
Security testing done differently
Most firms hand you a raw scanner dump and an invoice. We combine an AI testing engine with certified human validation — and we publish our prices.
AI-Accelerated
Our in-house engine, AI Bug Hunter, maps and tests your attack surface at machine speed — so nothing gets missed.
Human-Validated
Certified analysts verify every finding by hand. Nothing lands in your report until a human proves it's real — zero false positives.
Business-Logic Focus
We hunt the flaws that cause real financial damage — IDOR, auth bypass, workflow abuse — not just the ones scanners flag.
Transparent Pricing
Fixed, published prices — no hidden fees, no "call for a quote" games. You know the cost before you commit.
Audit-Ready Reports
Clear, prioritized reports mapped to ISO 27001, SOC 2, PCI-DSS & more — ready to hand to auditors and boards.
Research & Recognition
Published research on ISO 27001 & NIST, the NeuroShield framework, CAISR certification — and a UNGM-listed, SECP/PSEB-registered company behind every engagement.
How Our AI-Powered VAPT Works
AI-Accelerated Testing, Human-Validated Results
Our in-house engine (AI Bug Hunter) maps and tests your attack surface at scale; certified experts validate every finding. Nothing is reported until a human proves it.
MappingRecon & discovery
EngineAI Bug Hunter
PrioritizationSeverity & impact
ValidationCertified analysts
RemediationAudit-ready + retest
Aligned with PTES, OWASP & NIST · A signed Authorisation-to-Test and NDA are in place before any testing begins.
Inside the Engine
Our in-house AI testing engine — purpose-built to hunt the high-impact, business-logic flaws that generic scanners miss, with safety and human validation engineered in from the ground up. This is what you don’t get from an off-the-shelf tool.
Authorization-First by Design
The engine can't touch anything outside your signed scope. Every test action requires a single-use, signed grant — so testing stays controlled, auditable and safe.
Two-Brain Business-Logic Testing
A recon brain maps your app; a logic brain compares how it behaves across users and roles — surfacing IDOR/BOLA, auth-bypass and workflow abuse that scanners simply can't see.
Attack-Surface Mapping at Scale
Endpoints, parameters, roles and hidden entry points are discovered and tested at machine speed — far broader coverage than a manual-only team in the same time.
Built-In Network Safety
SSRF, DNS-rebinding and IP-pinning protections are baked into the worker — the engine can't be tricked into wandering off-target or harming systems outside scope.
Risk-Based Prioritization
Findings are scored by real business impact and exploitability — so you fix what actually matters first, not a 200-page list of low-severity noise.
Human-in-the-Loop, Always
The engine proposes; certified experts authorize and validate. Nothing reaches your report until a human proves it — so you get real findings, zero false positives.
The result: the speed and breadth of AI, with the judgement and accountability of senior human testers — on every engagement.
Inside AI Bug Hunter
One engine. Two brains.
Human-grade reasoning, machine-scale execution — our engine understands your application's logic, then works tirelessly to find the flaws that matter, and hands proof to a human.
- Reasons like a human — understands your app's logic, roles and workflows.
- Works like a machine — tests at scale, around the clock, without fatigue.
- Chains findings — surfaces IDOR, auth-bypass and workflow abuse others miss.
- Human-validated — certified analysts prove every result before your report.
Coverage
What we test
Full-stack coverage across everything your business runs on.
Transparent Pricing
Fixed prices. No hidden fees.
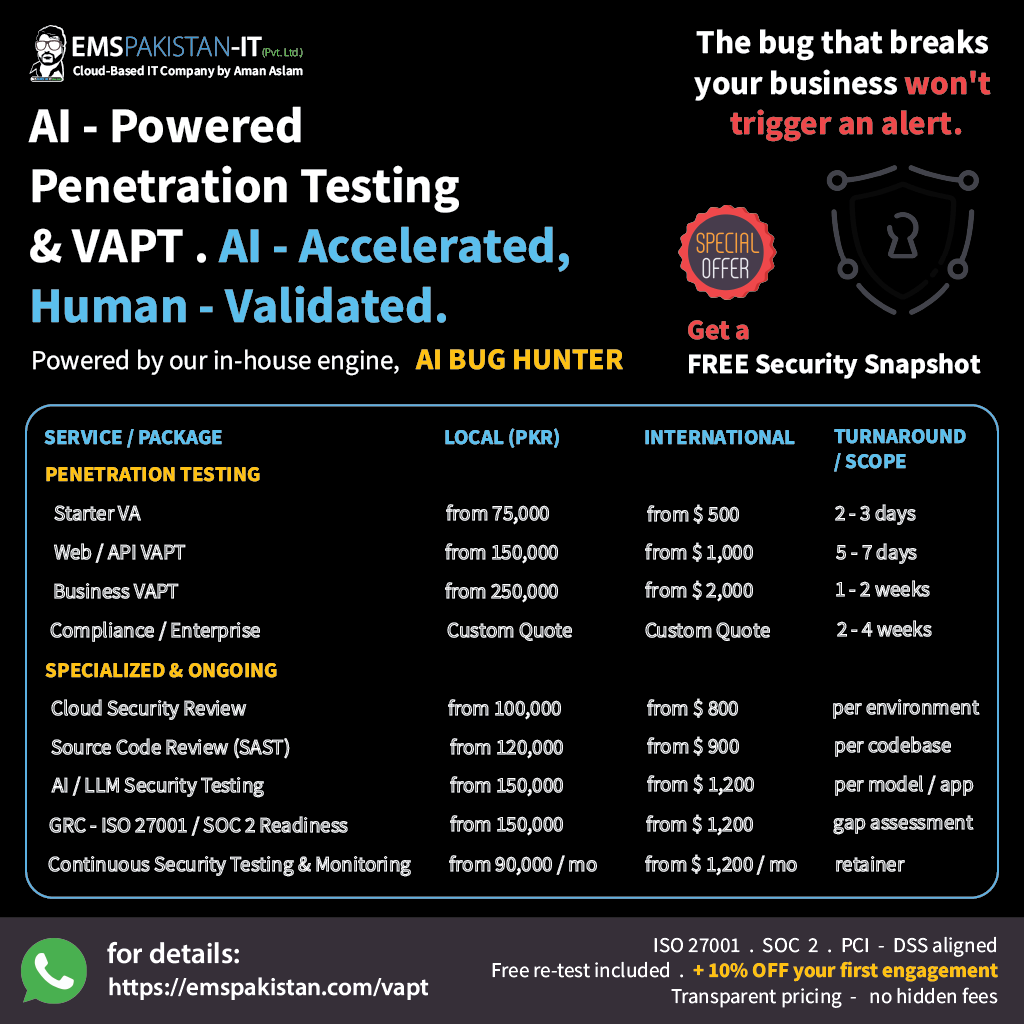
Local pricing for Pakistan, international pricing worldwide. Every engagement includes a full report, remediation guidance and a free re-test.
| Service / Package | Local (PKR) | International | Turnaround |
|---|---|---|---|
| Penetration Testing | |||
| Starter VA1 web/app · automated + light manual scan | from 75,000from $500 | from $500 | 2–3 days |
| Web / API VAPTFull manual pentest of one app + its API | from 150,000from $1,000 | from $1,000 | 5–7 days |
| Business VAPTMulti-asset, business-logic + compliance-ready | from 250,000from $2,000 | from $2,000 | 1–2 weeks |
| Compliance / EnterpriseBanks, govt, large multi-system scope | Custom Quote | Custom Quote | 2–4 weeks |
| Specialized & Ongoing | |||
| Cloud Security Review | from 100,000 | from $800 | per environment |
| Source Code Review (SAST) | from 120,000 | from $900 | per codebase |
| AI / LLM Security Testing | from 150,000 | from $1,200 | per model / app |
| GRC — ISO 27001 / SOC 2 Readiness | from 150,000 | from $1,200 | gap assessment |
| Continuous Security Testing & Monitoring | from 90,000/mo | from $1,200/mo | retainer |
New clients: 10% off your first engagement · 50% to start, balance on delivery · Prices exclude applicable taxes.
Getting Started
What we need from you to begin
Getting started is simple — you don't need any in-house security expertise. We guide you through each step, and most clients are ready to begin within a day or two.
Scope
The exact targets to test — website/app URLs, IP ranges, APIs, or systems — and anything to exclude.
Authorization-to-Test (ATT) letter
Your signed written permission confirming you're authorized to test the target. We never begin without it.
Signed NDA
So everything we find stays strictly confidential between us.
Test window
The days and hours you'd like testing to run — business hours, after hours, or a weekend.
Access credentials (if needed)
Test logins for authenticated testing. For a black-box test, none are required.
A point of contact
One person on your side we can reach for approvals or quick questions during the engagement.
Any special notes
Fragile systems, third-party services, rate limits, or compliance goals (ISO 27001, SOC 2, PCI-DSS) to keep in mind.
That's it — we handle the rest
Once these are in place, we agree the timeline and begin. We help you prepare each item along the way.
The easiest first step? Book your free Security Snapshot — we'll walk you through everything from there.
Get Your Free Security SnapshotAI-Powered Penetration Testing & VAPT Services Across Pakistan
We deliver AI-powered Penetration Testing, VAPT, and cybersecurity services for businesses in Islamabad, Lahore, Karachi, Rawalpindi, Faisalabad, and Peshawar, as well as international clients in the USA, Canada, UK, UAE, Australia, Indonesia, and Thailand.

Aman Aslam
Founder, EMSPakistan IT (Private) Limited
Aman Aslam is an Applied Scientist (SEO & AI Systems), Research Scholar, Information Security Professional and Full-Stack Software Developer who designs and builds secure, production-ready software—including AFIS-Lite—for organizations that need more than off-the-shelf products, develops generative AI models and integrates them into clients’ existing workflows, and at EMSPakistan IT (Private) Limited, leads research and development across AI Systems, SEO, AI Development, AI Security, and GRC. With 16+ years of hands-on experience across cybersecurity, AI, and software development, he is a CAISR-certified professional in AI Security & Risk and has published research on ISMS and ISO 27001 implementation. He leads the development of EMSPakistan’s in-house AI testing engine, AI BUG HUNTER, applying an authorization-first, human-validated approach to penetration testing and VAPT. His work spans applied research, technology innovation, cybersecurity governance, and AI-driven security systems, with scholarly contributions indexed across Google Scholar, ORCID, ResearchGate, Zenodo, Web of Science, and AD Scientific Index.
What You Get
Every engagement includes
Standards & Frameworks
Aligned with what auditors expect
Our testing and reporting map to the frameworks your business is measured against.
Frequently Asked Questions (FAQs)
A Vulnerability Assessment scans broadly and lists known weaknesses. A full penetration test goes further — our experts actively exploit those weaknesses, including business-logic flaws automated tools miss, to prove real-world impact. If you need compliance sign-off or real assurance, you want the full VAPT.
Our in-house engine, AI Bug Hunter, handles discovery and testing at scale — mapping your attack surface far faster than a human could. Certified analysts then validate every finding by hand. Nothing reaches your report until a human has proven it’s real, so you never chase false positives.
A Starter VA takes 2–3 days; a Web/API VAPT 5–7 days; a Business VAPT 1–2 weeks; and larger compliance/enterprise engagements 2–4 weeks. We agree the exact timeline with you before we start.
Yes. Once your team applies the fixes, we re-test to confirm each issue is closed — included in every engagement at no extra cost.
Yes — when properly authorised. Every engagement begins with a signed Authorisation-to-Test letter and NDA, and testing stays strictly within the scope you approve. Our process is authorization-first: no test runs against anything you haven’t explicitly approved, and we follow strict safety controls throughout.
No. All testing follows a signed Rules of Engagement, is scheduled around your business hours, and stays within an agreed, controlled scope — so your live operations keep running normally.
Yes — we serve clients across Pakistan, the UAE and internationally. International engagements are billed in USD at the rates shown above.
Our pricing is published openly on this page. A Starter VA begins at PKR 75,000, a Web/API VAPT at PKR 150,000, and Business VAPT from PKR 250,000. International clients are billed in USD. You always get a fixed-price proposal — no hourly surprises or hidden fees.
VAPT (Vulnerability Assessment & Penetration Testing) combines broad automated discovery with deep manual exploitation of your systems. Businesses need it to find and fix security gaps before attackers do, protect customer data, and satisfy compliance and customer security requirements.
At least once a year, and after any major change — a new app or feature, an infrastructure migration, or a merger. Many businesses also test on a compliance cycle (ISO 27001, SOC 2, PCI-DSS) or keep a continuous testing retainer for ongoing coverage.
Yes. Our reports map findings directly to ISO 27001, SOC 2, PCI-DSS, HIPAA, GDPR and PECA 2016 — so they’re ready to hand to auditors and to answer customer security questionnaires with confidence.
You receive an executive summary, a detailed technical report with proof and fix guidance, and a remediation call with our analysts. Once your team applies the fixes, we run a free re-test to confirm every issue is closed.
Getting started is simple — you don’t need any in-house security expertise. We just agree the scope (what to test), sign an Authorization-to-Test letter and NDA, and confirm a test window plus any login credentials needed for authenticated testing. We guide you through each step, so most clients are ready within a day or two. The easiest first step is to book your free Security Snapshot.
There’s no “pass” or “fail” — the goal is to find issues before attackers do. We prioritise every finding by real business impact, give you clear step-by-step remediation guidance, and then re-test to confirm the fixes worked. Finding issues now is exactly why testing is worth it.
A vulnerability scan is automated and only flags potential issues. Penetration testing adds skilled human testers who safely exploit those issues to prove what an attacker could actually do — so you learn not just “what could be wrong” but “how badly you could be breached.”
Penetration Testing & VAPT Terms & Conditions (Must Read)
- We operate globally, with 24/7 support.
- Free Security Snapshot first. To earn your trust, every new client receives a short, no-cost security snapshot of one target before any paid engagement — so you see the value before you commit.
- Authorized testing only. All testing begins only after a signed Authorization-to-Test (ATT) letter and NDA are in place. We test strictly within the scope you approve — nothing outside it.
- Payment terms: 50% upfront to begin, 50% on delivery of the final report. International clients are billed in USD; local clients in PKR.
- Free re-test included. After you apply the fixes, we re-verify the findings once at no extra cost.
- Reports and findings are kept strictly confidential and shared only with your authorized contacts.
- No work samples — by design. We do not share client work samples, reports, or case data. A firm that shows you another client’s data would just as easily share yours. Instead of asking clients to trust screenshots, we earn trust with a free, no-obligation Security Snapshot of your own target — so you judge our work on your systems, not someone else’s.
- Prices are fixed and transparent, exclusive of applicable taxes. New clients get 10% off their first engagement.
- Reseller-specific & other terms are available on our Terms & Conditions page.
Ready to find the bugs that matter?
Start with a free Security Snapshot — a no-cost look at your attack surface. New clients get 10% off their first full engagement.
Get Your Free Security Snapshot